
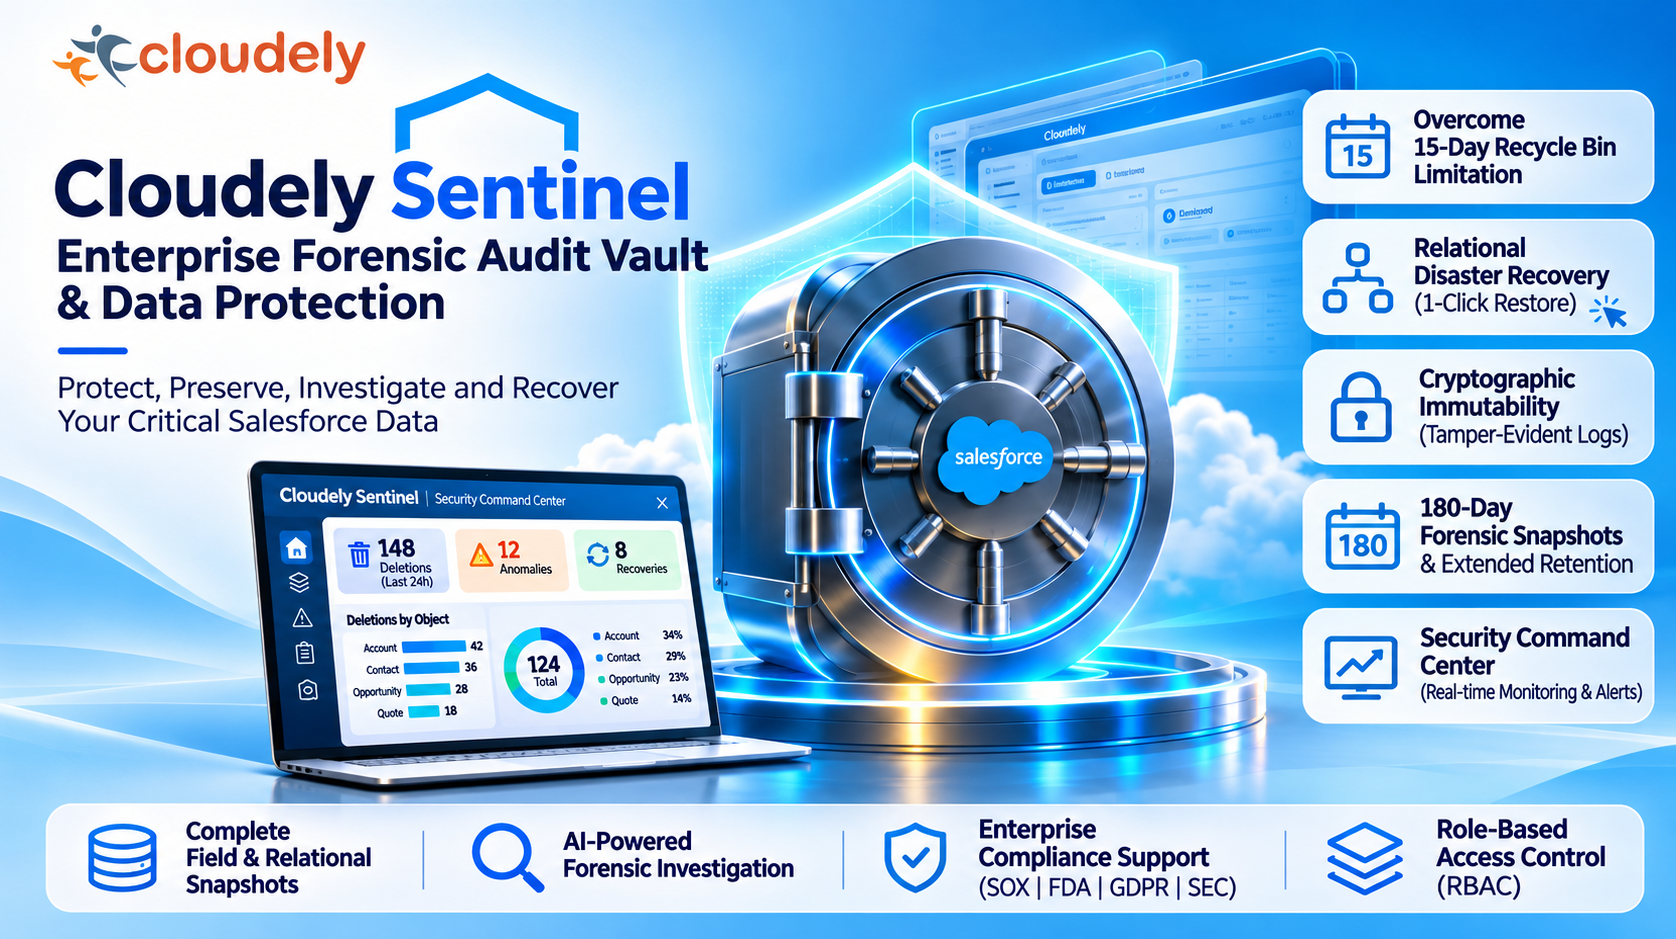
Introduction: Is Your Enterprise Prepared for Permanent Salesforce Data Loss?
Salesforce has become the operational backbone of modern enterprises. Organizations depend on it to manage customer relationships, sales opportunities, contracts, quotations, service operations, and mission-critical business processes.
But what happens when critical Salesforce records are accidentally deleted, maliciously modified, or permanently purged?
A deleted Account can impact associated Contacts, Opportunities, Quotes, and other dependent records. A seemingly routine administrative operation or integration error can create a cascading data-loss incident. Traditional audit trails may tell administrators that a record was deleted, but they may not preserve the complete historical record values required to reconstruct it.
This creates a critical gap between knowing that something happened and having the evidence and capabilities to recover what was lost.
Introducing Cloudely Sentinel – Enterprise Forensic Audit Vault & Data Protection.
Cloudely Sentinel is designed to strengthen Salesforce data protection through proactive forensic snapshots, cryptographic audit integrity, extended evidence retention, relational recovery, and centralized security intelligence.
It helps enterprises move beyond basic backup and deletion tracking toward a more comprehensive approach to data resilience, forensic investigation, and operational governance.
This approach strengthens Salesforce Data Protection by combining historical snapshots, audit integrity, and recovery capabilities.
The Hidden Salesforce Data Protection Challenge
Salesforce provides native data management and recovery capabilities. However, enterprises with complex data relationships, custom objects, integrations, and regulatory requirements may need additional protection beyond standard platform capabilities.
Salesforce Data Protection is essential for enterprises that need to safeguard critical business records and maintain reliable access to historical information.
Three challenges deserve particular attention.
1.The 15-Day Recycle Bin Limitation
Salesforce’s native Recycle Bin provides a temporary recovery window for eligible deleted records. Records that are permanently deleted or purged can no longer be recovered through the standard Recycle Bin experience.
For enterprises, this creates a recovery challenge when deletion incidents are discovered after the available recovery period.
2. Silent Relational Cascade Deletion
Enterprise Salesforce environments contain interconnected records.
For example, deleting a parent Account can affect associated business records depending on relationship configuration, deletion behavior, automation, and integrations.
The impact may extend to:
- Customer Contacts
- Sales Opportunities
- Quotes and commercial records
- Custom business objects
- Related operational records
Recovering an individual record without restoring its required relationships can leave the business with incomplete or inconsistent data.
3. Limited Historical Forensic Context
Knowing who deleted a record and when it happened does not necessarily explain what the record contained before deletion.
Field history tracking and audit logs have specific retention and coverage limitations. Enterprises may need a more comprehensive historical evidence repository containing complete record values, relationship information, and event metadata.
This is where a dedicated forensic audit vault becomes valuable.
Introducing the Cloudely Sentinel Protection Engine
Cloudely Sentinel introduces three complementary protection capabilities designed to strengthen enterprise Salesforce data resilience.
Capability 1: Complete Field and Relational Snapshots
Cloudely Sentinel is designed to capture structured snapshots of Salesforce records before critical deletion events.
These snapshots can include:
- Standard and custom object fields
- Record identifiers and metadata
- Parent-child relationships
- Related record references
- Deletion event timestamps
- User and integration context
By preserving complete JSON-based record representations, the platform can provide historical context that may not be available through standard audit records.
Capability 2: Cryptographic Immutability
Audit evidence is only valuable when organizations can establish its integrity.
Cloudely Sentinel incorporates a cryptographic protection approach designed to make audit records tamper-evident.
Potential capabilities include:
- Append-only audit event storage
- Cryptographic hashing
- Hash-chain verification
- Restricted administrative access
- Evidence integrity validation
- Auditable access to forensic records
The objective is to establish a trustworthy record of what happened, when it happened, and whether the evidence has been altered.
Capability 3: Extended Forensic Retention
Enterprise investigations and compliance reviews may occur long after the original business event.
Cloudely Sentinel introduces a proposed 180-day forensic snapshot retention capability, providing an extended historical evidence window beyond standard Salesforce deletion recovery.
Automated retention management can support:
- Scheduled evidence archival
- Retention policy enforcement
- Secure evidence retrieval
- Automated lifecycle management
- Controlled evidence disposal
Retention policies can be configured according to enterprise requirements and applicable legal obligations.
1-Click Relational Disaster Recovery
Restoring enterprise data is not simply about recovering a deleted record. It is about restoring the relationships and business context that make that record operationally useful.
Cloudely Sentinel introduces a relational disaster recovery approach designed to reconstruct deleted Salesforce records and their associated relationships.
How does it work?
Consider an enterprise customer account that is accidentally deleted.
The Account has five associated Contacts, three Opportunities, and two Quotes.
A traditional record-level recovery approach may require administrators to identify and restore each dependent record individually, validate relationships, and investigate missing data.
Cloudely Sentinel aims to simplify this process through a coordinated recovery workflow.
Step 1 – Identify the deletion event
Detect the deletion event and identify the affected parent record.
Step 2 – Retrieve forensic snapshots
Retrieve the preserved record snapshots from the secure forensic vault.
Step 3 – Analyse relational dependencies
Identify associated Contacts, Opportunities, Quotes, and other configured dependent records.
Step 4 – Reconstruct the relationship hierarchy
Determine the required restoration sequence and rebuild the relationships using the original Salesforce record identifiers wherever technically supported.
Step 5 – Execute controlled recovery
Allow authorised administrators to initiate a coordinated restoration process.
Step 6 – Validate recovery integrity
Verify record completeness, relationship consistency, and recovery outcomes.
The intended result is a simplified, auditable recovery experience that reduces manual restoration effort and helps minimise operational disruption.
Cloudely Sentinel Security Command Center
Enterprise administrators need more than a storage repository. They need visibility into what is happening across their Salesforce environment.
The Cloudely Sentinel Security Command Center is designed to provide a centralized operational view of data protection and forensic activity.
Key dashboard capabilities
| Feature | Business value |
|---|---|
| Deletion Monitoring | Visibility into deleted records |
| Anomaly Detection | Identify unusual deletion patterns |
| Recovery Monitoring | Track recovery operations |
| Audit Log Explorer | Investigate historical events |
| Object-Level Analytics | Understand deletion distribution |
| Access Control | Restrict forensic operations |
| Recovery History | Maintain restoration evidence |
Intelligent security monitoring
The solution can help security teams identify:
- Unusual deletion volumes
- Repeated deletion activity by specific users
- Unexpected integration-driven deletions
- High-impact parent record deletion events
- Suspicious access to forensic evidence
- Recovery failures and data integrity issues
By combining operational monitoring with historical evidence, Cloudely Sentinel aims to help enterprises transition from reactive incident investigation to proactive data protection.
Enterprise-Grade Recovery with Role-Based Access Control
Data recovery operations can introduce security risks if they are not properly governed.
Cloudely Sentinel incorporates a controlled recovery approach using Role-Based Access Control (RBAC).
Potential security controls include:
- Custom Salesforce permissions
- Dedicated forensic administrator roles
- Recovery approval workflows
- Separation of duties
- User-level recovery activity logs
- Restricted access to sensitive snapshots
- Recovery execution audit trails
For example, a Salesforce administrator may be allowed to investigate a deletion event, while only an authorised recovery operator can initiate restoration.
This helps ensure that powerful recovery operations remain governed and traceable.
Enterprise Compliance and Audit Readiness
Organizations operating in regulated industries must demonstrate appropriate controls over data access, retention, security, and evidence management.
Cloudely Sentinel is designed to support enterprise audit and compliance programmes through structured evidence preservation and controlled access.
Potential regulatory alignment areas include:
SOX – Section 404
Supports internal control evidence collection, audit traceability, and accountability for relevant business data operations.
FDA – 21 CFR Part 11
Provides capabilities that may support electronic record integrity, audit trail controls, and access governance when implemented with the required validated procedures and controls.
GDPR – Article 30
Can support the maintenance of records and evidence relevant to processing activities, subject to the organisation’s broader privacy governance obligations.
SEC / FINRA
Can support evidence preservation and auditability requirements relevant to applicable recordkeeping obligations, depending on the organisation’s regulatory classification and retention policies.
Importantly, Cloudely Sentinel is a data protection and audit support solution, not an automatic compliance certification. Regulatory compliance requires appropriate organisational policies, validated technical controls, and documented operating procedures.
Cloudely Sentinel: Key Business Benefits
Cloudely Sentinel is designed to deliver measurable business value across data resilience, security operations, and enterprise governance.
| Business area | Expected benefit |
|---|---|
| Data Protection | Preserve critical Salesforce record history |
| Disaster Recovery | Simplify relational record restoration |
| Audit Integrity | Improve confidence in historical evidence |
| Security Operations | Improve deletion and anomaly visibility |
| Compliance | Support audit evidence availability |
| Administration | Reduce manual investigation and recovery effort |
| Business Continuity | Minimise the impact of data-loss incidents |
Proposed solution performance targets
The product concept includes the following target capabilities, which should be validated through performance testing and production architecture assessment.
- 180 Days: Proposed forensic snapshot retention.
- Less than 650 ms: Target relational recovery time for the demonstrated recovery scenario.
- 100%: Target relational integrity for supported recovery scenarios.
- 714x: Demonstrated schema-description caching improvement in the referenced benchmark.
Actual performance will depend on record volumes, Salesforce API limits, relationship complexity, automation, infrastructure, and transaction size. These figures should be treated as validated benchmarks only after reproducible testing.
Why Enterprises Need More Than Traditional Salesforce Backup
Traditional backup solutions primarily focus on preserving data and enabling restoration.
Cloudely Sentinel extends this concept by combining forensic evidence preservation, audit integrity, relational recovery, and security monitoring.
The distinction is important:
| Traditional backup approach | Cloudely Sentinel vision |
|---|---|
| Periodic backup | Event-driven forensic snapshots |
| Record restoration | Relational recovery |
| Historical data storage | Cryptographically verifiable evidence |
| Basic deletion visibility | Centralised security intelligence |
| Manual investigation | Guided forensic investigation |
| Backup administration | Governed recovery operations |
Cloudely Sentinel is intended to complement an enterprise’s broader backup, disaster recovery, identity management, and security ecosystem rather than replace every existing control.
Built for Complex Salesforce Enterprise Environments
Cloudely Sentinel is particularly relevant for organisations with:
- Large Salesforce implementations
- Complex parent-child object relationships
- Multiple integration platforms
- High-volume transactional data
- Distributed Salesforce administrator teams
- Strict audit and data retention requirements
- Mission-critical customer and revenue operations
Potential integration areas include Salesforce Sales Cloud, Service Cloud, Revenue Cloud, Data 360, Agentforce, enterprise integration platforms, and external security monitoring systems.
This creates an opportunity to establish a consistent data protection and forensic governance layer across critical enterprise workflows.
The Cloudely Advantage
Cloudely brings Salesforce consulting, enterprise architecture, Revenue Cloud, Data 360, and Agentforce implementation expertise to the development of enterprise-grade solutions.
With Cloudely Sentinel, the objective is to extend this expertise into a focused data protection and forensic intelligence capability.
The platform’s vision is straightforward:
- Protect critical enterprise records before they are lost.
- Preserve evidence beyond standard recovery windows.
- Reconstruct complex relational data with confidence.
- Maintain tamper-evident audit records.
- Improve security visibility through a centralized command center.
- Enable controlled and traceable recovery operations.
Conclusion: Move from Data Recovery to Enterprise Data Resilience
Data loss is not always immediately visible. A deletion event may go unnoticed for days or weeks, and by the time an organisation identifies the impact, its standard recovery options may no longer be available.
Enterprises need a proactive approach that combines historical evidence, data protection, relational recovery, and security governance.
Cloudely Sentinel – Enterprise Forensic Audit Vault & Data Protection is designed to address this challenge.
By bringing together forensic snapshots, cryptographic audit integrity, extended retention, relational disaster recovery, and a centralized security command center, Cloudely Sentinel aims to help organisations protect their most critical Salesforce business information.
Don’t just track what was deleted. Preserve what existed, understand what happened, and recover what matters.
Cloudely Sentinel by Cloudely
Protect. Preserve. Investigate. Recover.
Strengthen Your Salesforce Data Protection Strategy
Your Salesforce data is one of your organization’s most valuable assets. Protecting it requires more than routine backups. It requires visibility, accountability, investigation, and a reliable recovery strategy.
Discover how Cloudely Sentinel can help your organization strengthen its Salesforce data protection, forensic investigation, and disaster recovery approach.
Interested in Learning More About Cloudely Sentinel?
Have questions or want to discuss your enterprise Salesforce data protection requirements? Get in touch with our team.
Submit your inquiry using the form below: